PCI DSS / A-EP
For e-commerce merchants whose website affects payment security without itself receiving account data.
Who it is for
SAQ A-EP covers eligible online stores that outsource payment processing to a compliant provider while retaining control over website elements or functions affecting the transaction. The distinction from SAQ A depends on the actual data flow and the origin of payment page elements.
Key eligibility criteria
- This validation path applies only to e-commerce.
- The website does not receive account data but can affect transaction security or the integrity of the page collecting it.
- Payment processing is outsourced to a PCI DSS-validated provider. Payment page elements originate from the merchant website or compliant providers.
- The merchant does not electronically store account data. Every other eligibility criterion in the current SAQ A-EP must also be confirmed.
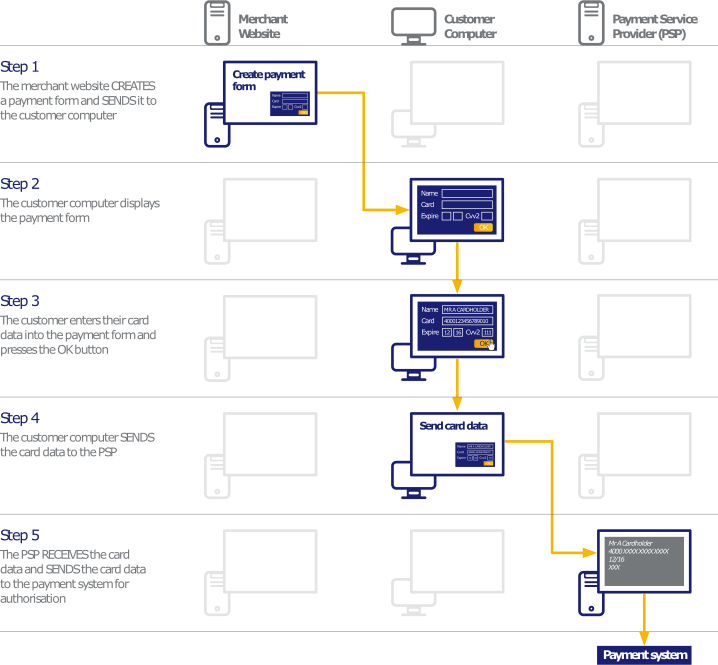
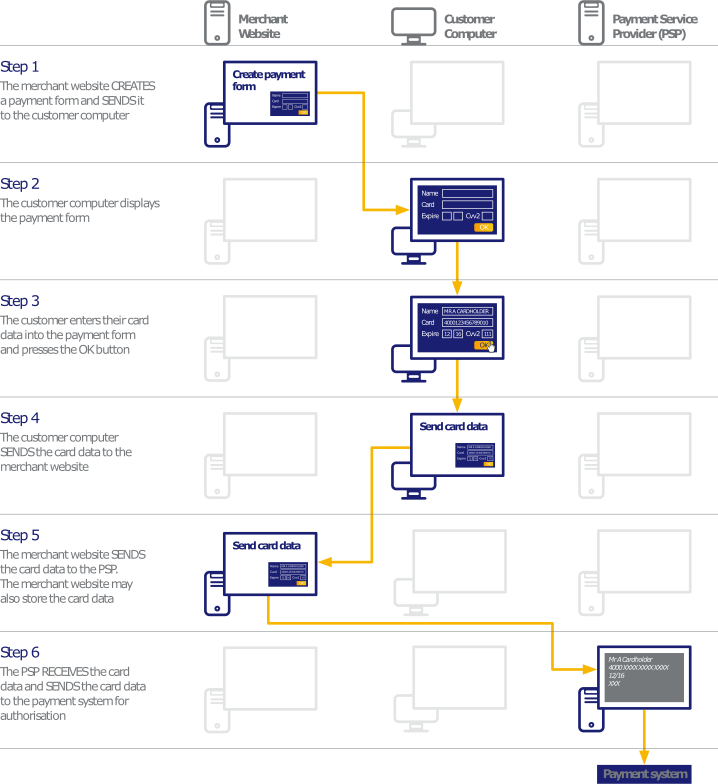
Payment flow
- 01Merchant website
- 02Payment page with external provider
- 03Processing and confirmation
Illustrative overview. Your actual data flow must be reviewed before choosing an SAQ.
Before completing your SAQ
Document who hosts the site, who changes its code and which scripts participate in payment. Collect the data flow and provider evidence to confirm whether SAQ A, A-EP or another path applies.
These criteria are a summary and do not replace the complete questionnaire. Confirm every criterion in the applicable version and the validation method with your acquirer or accepting entity.