PCI DSS / D
For merchants eligible for self-assessment that do not meet the criteria for another SAQ type.
Who it is for
SAQ D for Merchants covers broader or complex payment environments. It can apply to businesses that store electronic account data, handle it on their own systems or do not fully qualify for another path. It is a different document from SAQ D for service providers.
Key eligibility criteria
- The merchant has confirmed with the accepting entity that it may use an SAQ rather than another assessment method, such as a ROC.
- The assessed environment does not meet every criterion for another SAQ type.
- Scope includes systems storing, processing or transmitting account data, along with connected systems and systems affecting their security.
- Requirements are reviewed against the actual environment. SAQ type and merchant Level are different concepts; Level alone does not select the questionnaire.
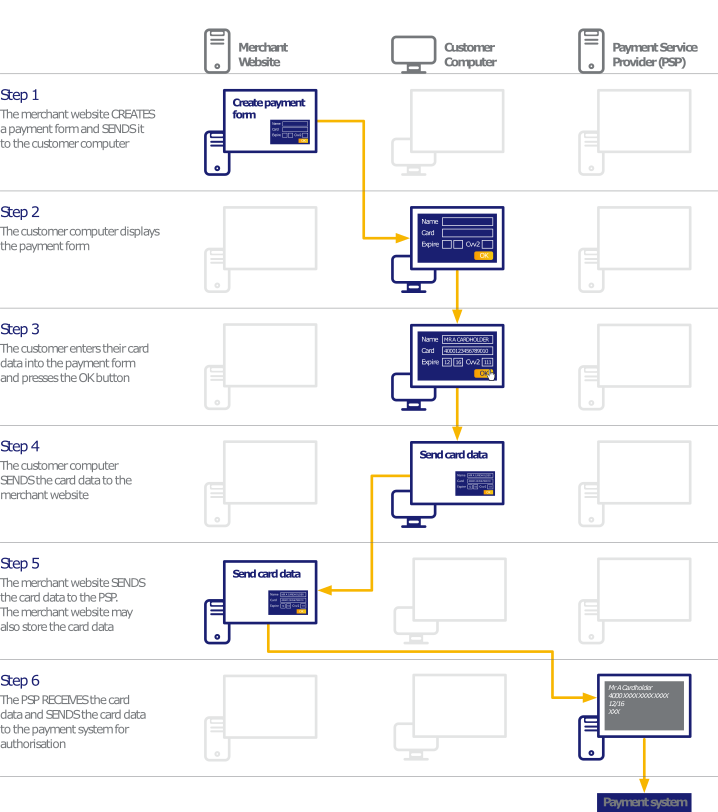
Payment flow
- 01Payment acceptance channels
- 02In-scope systems
- 03Processor and confirmation
Illustrative overview. Your actual data flow must be reviewed before choosing an SAQ.
Before completing your SAQ
Start with a system inventory, data flows and every payment channel. Document providers, access and storage locations. Organise a gap assessment and supporting evidence so that answers reflect actual controls.
These criteria are a summary and do not replace the complete questionnaire. Confirm every criterion in the applicable version and the validation method with your acquirer or accepting entity.