PCI DSS / A
For merchants that fully outsource account data handling to external providers for card-not-present transactions.
Who it is for
SAQ A covers eligible e-commerce and mail or telephone order merchants. The business relies on providers with validated PCI DSS compliance and does not handle electronic account data on its own systems.
Key eligibility criteria
- Acceptance is limited to card-not-present transactions, with all account data functions outsourced to appropriate external providers.
- The merchant does not electronically store, process or transmit account data on its systems or premises.
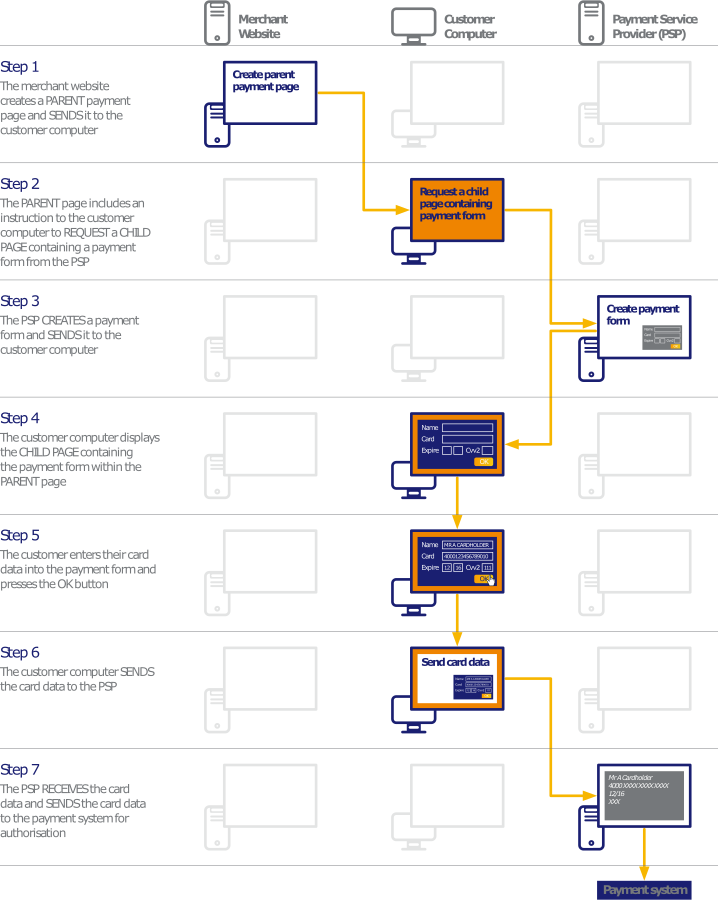
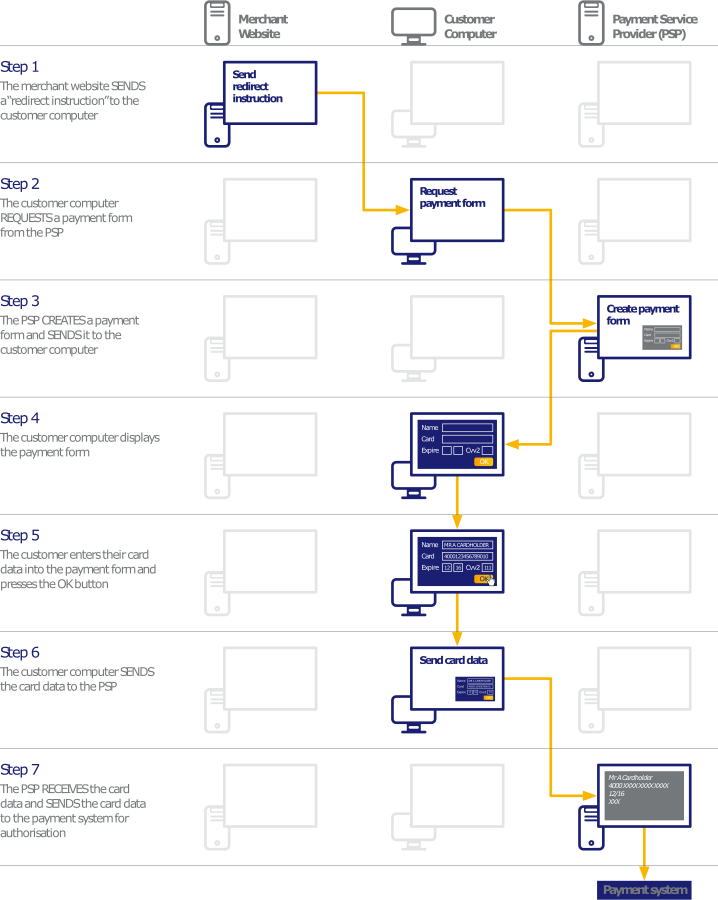
- For e-commerce, payment page elements originate only and directly from a compliant provider. The actual redirect or embedded implementation must be assessed as a whole.
- For embedded payment forms, the current eligibility criterion concerning protection against script attacks must also be considered. An iframe alone does not establish eligibility.
Payment flow
- 01Customer order
- 02Payment with external provider
- 03Confirmation to merchant
Illustrative overview. Your actual data flow must be reviewed before choosing an SAQ.
Before completing your SAQ
Collect provider details, their compliance evidence and a description of how the website connects to payment. Check that card details do not reach your logs, email, forms or other systems.
These criteria are a summary and do not replace the complete questionnaire. Confirm every criterion in the applicable version and the validation method with your acquirer or accepting entity.